NEWDigital Investigation & Cybercrime
We find out who is behind it, with method, traceable sources and full confidentiality.
We track and collect information from open, deep and dark sources, in a lawful, documented way: fake profiles, hidden links, scammers and incident response, to anticipate threats and identify cybercriminals.
What it is
Intelligence from open sources, with method and a legal basis.
OSINT (Open Source Intelligence) is investigation based on lawfully accessible information: social media, websites, public records and official databases, plus deep and dark web forums. Handled with method, these leads reveal who is behind fake profiles, scams and attacks, and become usable evidence.
Intelligence
We cross-reference patterns, accounts, metadata and digital footprints to link profiles to people.
Tracking
We follow trails across open sources and the deep and dark web, recording every source consulted.
Identification
We reach the people responsible and deliver a report ready for legal action.
When to reach out
It makes sense for you if you've ever said one of these
We serve companies, law firms and individuals. Want to gauge your risk first? Take the scam check →
What we deliver
One investigation, stage by stage
The 10 deliverables of a full investigation, organized over up to 12 weeks. The actual timeline depends on the case scope.
Scope and initial collection
Understand the case, define the purpose and legal basis, and gather the initial evidence.
IDENTIFICATION CONFIDENCE · SCALE OF 1 TO 5
2,4 by the end of stage 1
Illustrative example. Results depend on the evidence available.
How it works
From first report to final report.
- PHASE 1
Assessment
We hear the case, review the initial evidence and define the purpose and legal basis.
- PHASE 2
Collection
We gather information from open sources and the deep and dark web, preserving every piece of evidence.
- PHASE 3
Analysis
We cross-reference data, map links and identify those responsible.
- PHASE 4
Report
We deliver the technical report and support the legal next steps.
Engagement models
Choose the format your case needs.
Pricing on request, based on scope and complexity.
ESSENTIAL
For a one-off check
- Scope and legal basis
- Locating individual and company IDs and phones
- Tracing emails and WhatsApp numbers to owner ID
- Summary report with guidance
COMPLETE
Full investigation
- Everything in Essential
- Deep and dark web and leaks
- Background check and link map
- De-anonymization of fake profiles
- Technical report and legal support
ON DEMAND
For law firms and companies
- Technical report
- Due diligence and background checks
- Support for ongoing cases
- Private investigation
Comparison
Investigate on your own or with specialists?
Who leads the investigation
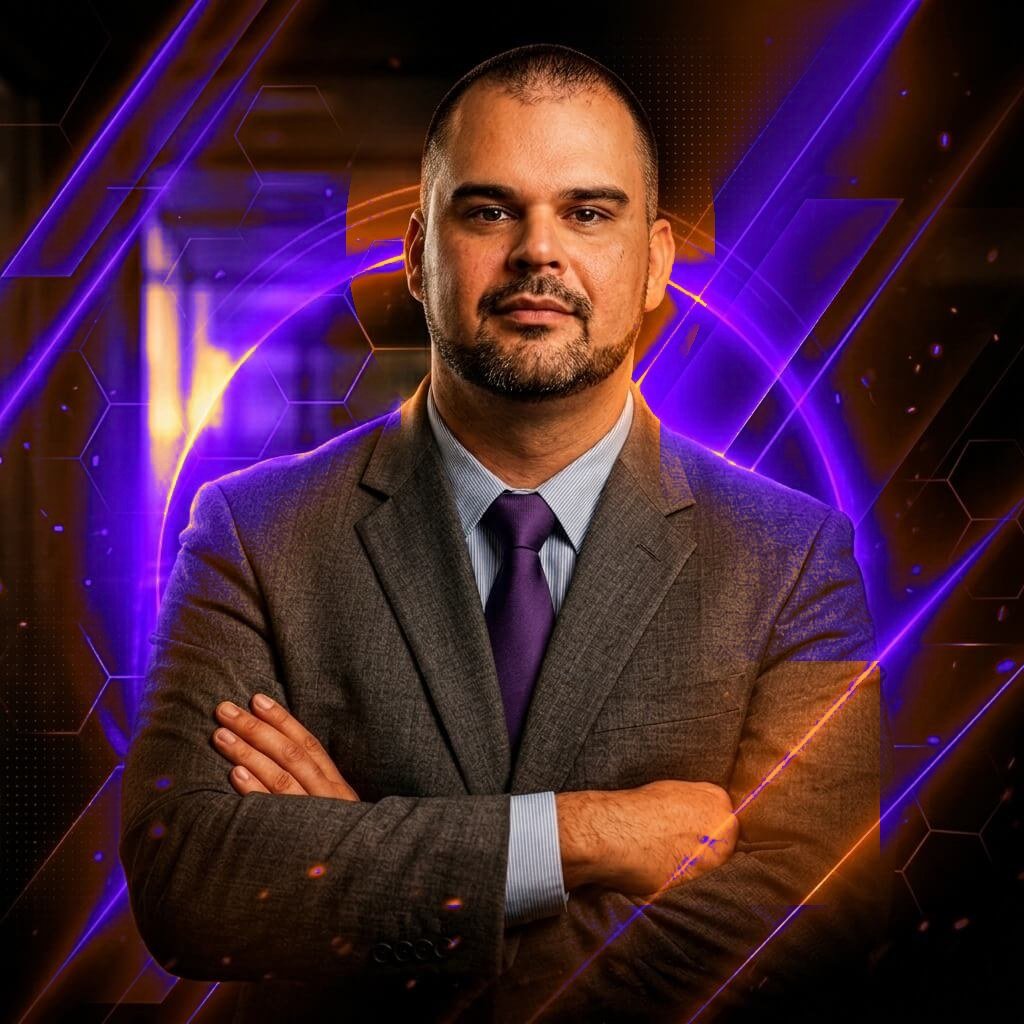
Felippe Britto
CISO · Head of Cybersecurity & Digital Investigation · 28 years of experience
He has led information security and incident response in banking, manufacturing, government and services, with training in cyber forensics and ethical hacking. He runs every investigation with method, ethics and a focus on evidence.
FAQ
Questions about digital investigation
It is investigation based on open sources — social media, websites, public records and official databases — and, when needed, deep and dark web forums. Every piece of information is collected lawfully, recorded and cited in the report.
The CiBER DETETiVE ecosystem
One team to investigate and protect
All 8 practice areas work together, with the same team and the same standard of confidentiality. Combine the ones your case needs.